Governance Risk and Compliance
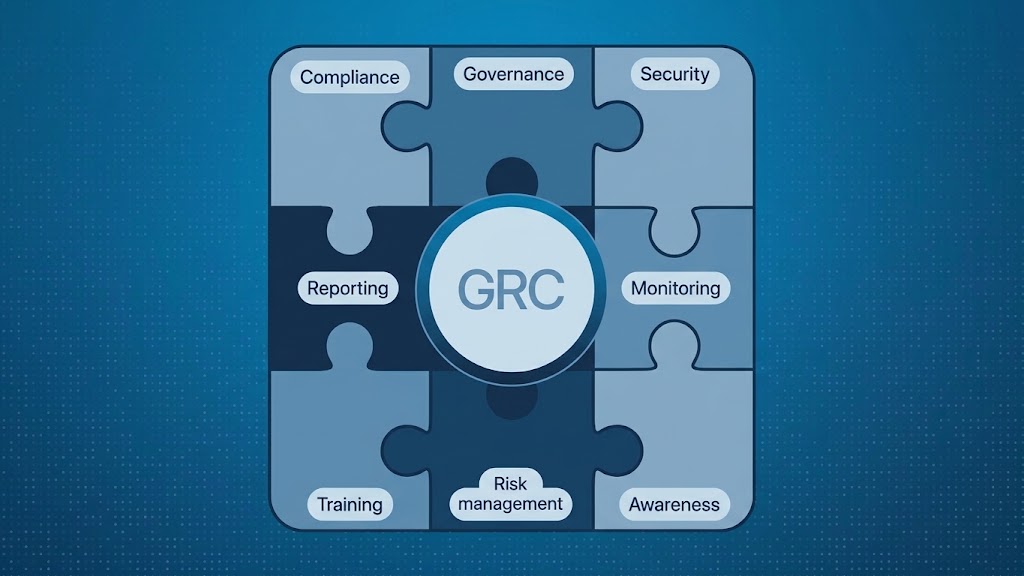
What Is Governance, Risk & Compliance?
GRC stands for Governance, Risk and Compliance.
It is the way an organisation brings together its rules, responsibilities, risks and legal or regulatory requirements so that it can operate effectively and make informed decisions.
Governance is about how an organisation is directed and controlled. It covers who is responsible for decisions, how policies are set and how the organisation makes sure its objectives are being met.
Risk is about identifying what could go wrong, understanding the potential impact and deciding what needs to be done to reduce or manage that risk.
Compliance is about making sure the organisation meets the laws, regulations, standards, policies and contractual requirements that apply to it.
Good GRC connects these areas rather than treating them separately. It helps an organisation understand what it needs to achieve, what could prevent it from doing so and what requirements it must meet along the way.
In cybersecurity, GRC applies the same approach to protecting information, systems and services.
It helps organisations understand their cyber risks, put appropriate security controls in place and show that they are meeting recognised standards, regulations and customer requirements.
GRC can include activities such as risk assessments, security policies, staff responsibilities, supplier reviews, incident management, audits and maintaining evidence that security controls are working.
Important Frameworks / Standards for UK organisations
Cyber Essentials
Cyber essentials is a UK Government backed certification scheme designed to protect organisations against common cyber attacks. It focuses on five key technical controls covering firewalls, secure configuration, security updates, user access and malware protection.
ISO/IEC 27001
ISO27001 an international standard for information security management. It requires organisations to identify information security risks, select appropriate controls and continually review and improve how information security is managed.
SOC2
SOC 2 is an assurance framework commonly used by service organisations. An independent auditor examines controls relating to areas such as security, availability, processing integrity, confidentiality and privacy. The resulting SOC 2 report can give customers and other stakeholders assurance about how those controls are designed and operated.
Please complete the form below to find out more.
What Our Clients Say
“CyberWhite have been a pleasure to deal with by repeatedly demonstrating their professionalism and technical knowledge throughout the procurement process and execution of our project. From initially exploring our goals to a consultant working with us on-site and remotely, we’ve enjoyed a positive experience that has ultimately benefited our organisation and helped to improve our Cyber Security posture.”
“I would like to say a thousand “thank you’s” to CyberWhite after rescuing us from the commercial disaster we faced after being subjected to a very sophisticated fraud. Without the timely involvement and expertise from CyberWhite, we would undoubtedly have faced catastrophic consequences including a significant financial loss and possibly a forced closure of the business. We will always remember the kindness and professional approach taken by the CyberWhite team. They were able to successfully recover the critical data which was the life blood of our business. This expertise has allowed us to continue trading and provided us with the additional benefits of ensuring that we are more cyber risk aware and we now have a security partner to support us.”
“As an Operator of Essential Services, PX Group comply with advice provided by recognised security bodies such as NCSC. The advice is relevant to all organisations who provide infrastructure or support to the UK’s critical national infrastructure. PX Group engaged CyberWhite to undertake Third Party Security Audits (aligned to ISO28000:2007) against key suppliers who had access to information assets within the PX Group domain. CyberWhite created a comprehensive audit document set and supported this with interviews and visits in order to validate responses. The output from CyberWhite was comprehensive and provided security assurance to PX Groups stakeholders and interested parties that the key suppliers had a focus on security and understood and could demonstrate best practices in relation to the handling of PX Groups information assets. This process has been invaluable in validating what we believed and providing a platform from which we will continue to assess, review and benchmark all parties in our information supply chain.”